
TOKYO - A core member of the international ransomware group Qilin was detained in Japan and handed over to German authorities, according to people familiar with the case, as Japanese companies and institutions face a growing wave of cyberattacks that has exposed nearly 15 million pieces of personal information this month alone.
Concern is mounting in Japan's business community as unauthorized access and data leaks are reported almost daily. Cybersecurity research has also found that attackers are increasingly making active use of artificial intelligence, with such activity rising 56% from a year earlier.
GMO Internet Group said on October 7 that information including names and telephone numbers of up to 940,000 people may have been leaked from a survey website operated by a subsidiary. Actual financial damage was also confirmed, with points worth around 3 million yen held by some users fraudulently exchanged for Amazon gift codes.
Discount retailer MrMax also announced a possible leak involving information on about 1.73 million people, while Citizen Watch said personal information relating to around 100,000 people may have been compromised.
Osaka University, meanwhile, suffered a major system failure that forced all classes to be canceled. At least 130,000 sets of personal information were stored on the affected servers, potentially including photographs used on student identification cards.
The number of records potentially affected by incidents disclosed in October has reached roughly 15 million.
Cybersecurity experts say one reason for the rapid increase is the spread of AI tools that can automate and dramatically accelerate attacks. A person who previously might have been able to carry out only around 1,000 attacks a day could potentially launch about 1 million attacks in the same period by using AI to build more efficient programs, according to one expert.
The growing threat has also highlighted the role of hacker groups operating across national borders.
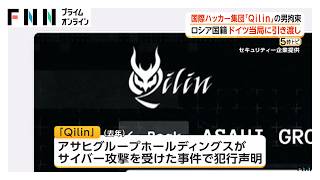
One of them is Qilin, a ransomware group blamed for an attack on Asahi Group Holdings in September last year. The attack caused a large-scale system failure at the beverage group, temporarily disrupting production and shipments.
Nearly a year later, it has emerged that a central Qilin member was detained in Japan.
According to people familiar with the matter, a 28-year-old Russian national believed to be a key member of the group was taken into custody in Osaka in May and subsequently handed over to German authorities.
German investigators had been seeking the man on suspicion of illegally obtaining and encrypting data from a German logistics company in September last year and extorting cryptocurrency worth around 26 million yen in return for restoring access.
In May, investigators examining Qilin's activities accessed the group's dark-web site with cybersecurity specialists. The site contained personal information and other material believed to have been stolen from Asahi Group.
When the group was contacted at the time, a response attributed to Qilin said that large companies such as Asahi could spend millions of dollars on cybersecurity but that the outcome demonstrated that no method could completely prevent cyberattacks.
Following the detention of the suspected core member, another message was sent to Qilin seeking answers on whether the group had been involved in information leaks affecting major Japanese companies, including Daiwa Securities and other businesses, how it viewed the detention of one of its members in Japan, and whether it was connected to the recent series of cyberattacks in the country.
The account appeared to be online immediately after the message was sent, but no response had been received.
The repeated breaches are also prompting consumers to reconsider how they protect themselves online. Some people said they were trying to use more complicated passwords, avoid predictable combinations and refrain from using information such as birthdays.
One man said he began taking additional precautions after receiving an email informing him that information associated with his Times Car account had been leaked. He subsequently contacted credit-related organizations and applied for protective measures intended to reduce the risk of fraudulent use of his identity.
Parents are also becoming more cautious about the applications their children install. One parent said that when a child asks to download an app because friends are using it, the family first checks the reliability of the service through internet searches and AI tools before deciding whether to allow it.
Digital affairs minister Furukawa urged individuals on October 7 to stop reusing passwords and instead set a different password for each service.
While such measures can be inconvenient because users must remember numerous passwords, cybersecurity specialists have long warned against easily guessed combinations such as keyboard sequences or simple alphabetical strings.
Awareness of such risks has been high in the United States for more than a decade, following repeated cases in which personal information was leaked from social media platforms and other online services.
Experts say individuals should also consider services offered by credit information agencies that allow people to register alerts when identity documents or other sensitive information have been exposed. Such registrations can prompt additional checks if someone attempts to take out a loan or make another financial application using a stolen identity.
Demand for such services has recently risen sharply in Japan, in some cases making it difficult for consumers to get through to credit information agencies.
The succession of breaches involving even major companies is reinforcing concerns that no organization can guarantee complete protection from cyberattacks, increasing pressure on businesses to strengthen security while requiring individuals to take greater responsibility for protecting their own information online.
Source: TBS